
What is Gemini 3.5 Flash Cyber
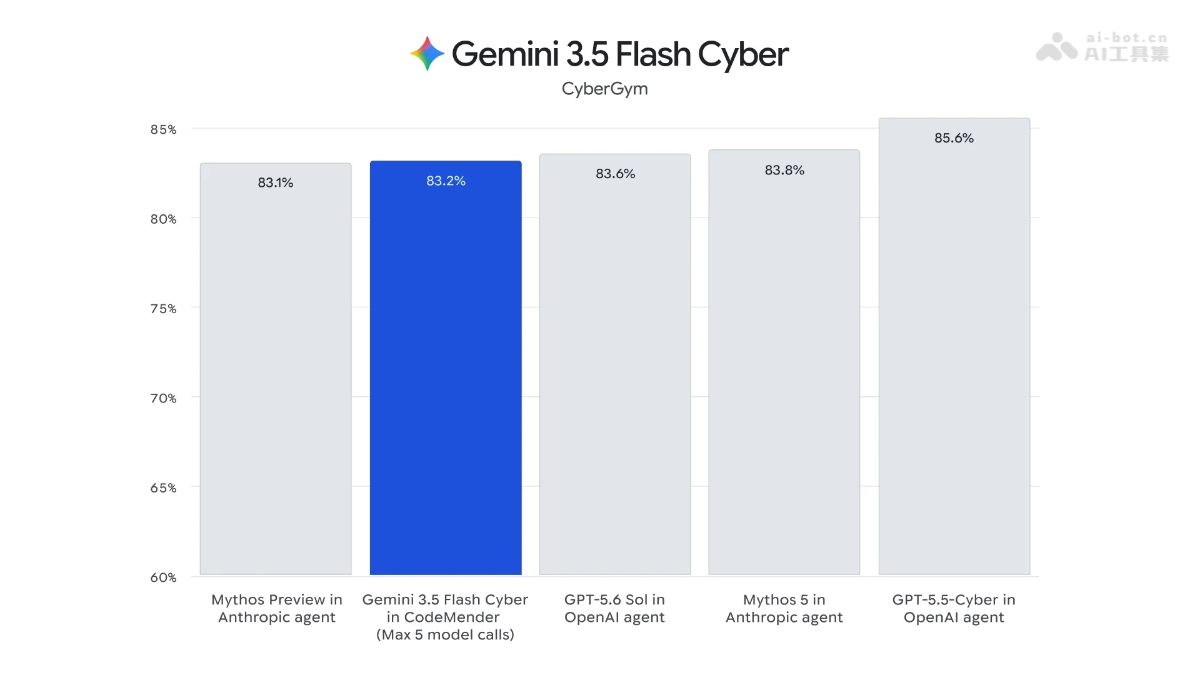
Gemini 3.5 Flash Cyber is a cybersecurity-specialized model fine-tuned by Google based onGemini 3.5 Flash , and used in pairing with the CodeMender code security agent, specializing in vulnerability discovery and remediation. The model adopts a multi-agent collaboration architecture, in which multiple agents work together to generate a unified security report. It reaches frontier-level performance on the CyberGym benchmark, and its cost per token is lower than that of larger models. Given dual-use risks, it is currently open only to governments and trusted partners.
Main features of Gemini 3.5 Flash Cyber
-
Vulnerability scanning: The model can automatically scan codebases and identify potential security vulnerabilities and risk points.
-
Vulnerability remediation: For discovered vulnerabilities, the model generates remediation suggestions and patch code, and verifies their effectiveness.
-
Security reports: Through the multi-agent collaboration architecture, it aggregates analysis results and outputs a unified, structured security report.
-
Batch auditing: It processes massive amounts of code in a low-cost, high-throughput manner, supporting enterprise-grade security scanning and CI/CD pipeline integration.
-
Risk rating: It prioritizes and assesses the impact of detected vulnerabilities, helping defenders allocate remediation resources rationally.
Technical principles of Gemini 3.5 Flash Cyber
- Model foundation: Cybersecurity-specialized fine-tuning is performed based on the Gemini 3.5 Flash architecture, inheriting its efficient token utilization and low-latency characteristics, and training on cybersecurity corpora such as vulnerability databases, CVE reports, and security patches.
- Multi-agent collaboration architecture: Multiple Flash Cyber agents run collaboratively through the CodeMender platform. Detection agents scan code to identify vulnerabilities, verification agents reproduce and rule out false positives, remediation agents generate patches and test compatibility, and aggregation agents integrate and output a unified security report.
- Efficiency optimization: It uses the efficient reasoning capabilities of the Flash series to reduce token consumption, and multi-agent parallel processing shortens the security audit cycle, achieving a lower cost per token than larger-parameter models.
- Safety alignment: Safety constraints are embedded during training to prevent the model from being induced to generate offensive code, and output-layer filtering mechanisms ensure that only defensive remediation suggestions are returned, while dual-use risks are managed through a limited-access pilot.
How to use Gemini 3.5 Flash Cyber
The model is not open to the public. Only government agencies and vetted trusted partners may apply to participate in the limited-access pilot program.
Core advantages of Gemini 3.5 Flash Cyber
- Cost leadership: Based on the Flash architecture, it achieves efficient reasoning, with cost per token significantly lower than competing models with larger parameter scales, making it suitable for enterprise-grade large-scale security auditing.
- Multi-agent collaboration: CodeMender has four built-in types of agents—detection, verification, remediation, and aggregation—working collaboratively to automatically complete the full closed loop from vulnerability discovery to report generation, reducing manual intervention.
- Frontier performance: It reaches the industry's top tier in the CyberGym benchmark test, placing it in the same competitive range as the specialized security agents from Anthropic and OpenAI.
- Fast response: It inherits the low-latency characteristics of the Flash series, generating vulnerability scans and remediation suggestions quickly, shortening the security response time window.
- Controllable risk: Adopt a limited-access pilot strategy, opening it only to governments and trusted partners, strictly preventing dual-use abuse while providing defensive capabilities.
Comparison of Gemini 3.5 Flash Cyber with Similar Competing Products
| Dimension | Gemini 3.5 Flash Cyber | Anthropic Mythos Preview |
|---|---|---|
| Positioning | A cybersecurity-specific model, paired for use with the CodeMender code security agent | A security research-specific model, integrated into the Anthropic agent framework |
| CyberGym Score | 83.2% (under the CodeMender architecture) | 83.1% (under the Anthropic agent architecture) |
| Model Base | Fine-tuned based on Gemini 3.5 Flash | The specific base model has not been disclosed |
| Architectural Features | Multi-agent collaboration (coordination among detection, verification, remediation, and summarization agents) | Whether the architecture is single-agent or multi-agent has not been clearly disclosed |
| Cost Advantage | Lower cost per token than larger-parameter models, emphasizing the efficiency of the Flash series | Specific pricing and cost data have not been disclosed |
Application Scenarios of Gemini 3.5 Flash Cyber
- Enterprise Code Security Auditing: Automatically scans large codebases for vulnerabilities and assesses risk, reducing the cost of manual security review.
- CI/CD Pipeline Integration: Automatically performs security checks before software release, blocking vulnerable code from entering the production environment.
- Open Source Dependency Security Screening: Scans third-party libraries and dependencies referenced by projects to identify known CVE vulnerabilities and supply chain risks.
- Security Incident Emergency Response: After a vulnerability disclosure, quickly locates the scope of affected code, generates remediation patches, and verifies their effectiveness.
- Government Critical Infrastructure Protection: Provides targeted security testing for government systems and critical infrastructure to safeguard national-level cybersecurity.