
What is Aardvark
Aardvark is an agent launched by OpenAI based on GPT-5 that can automatically discover and fix security vulnerabilities in code. Aardvark continuously analyzes source code repositories to identify vulnerabilities, assess exploitability, classify severity levels, and propose targeted remediation plans. Aardvark uses a multi-stage workflow, including analysis, commit scanning, validation, and remediation, and can read code, write tests, and verify vulnerabilities like a human security researcher. Aardvark seamlessly integrates with GitHub and existing workflows, supports human review, and ensures the accuracy of remediation plans. The emergence of Aardvark pioneers a new "defender-first" paradigm, providing an efficient and automated new solution for software security. Aardvark is now in closed beta; filling out an application can grant early access.
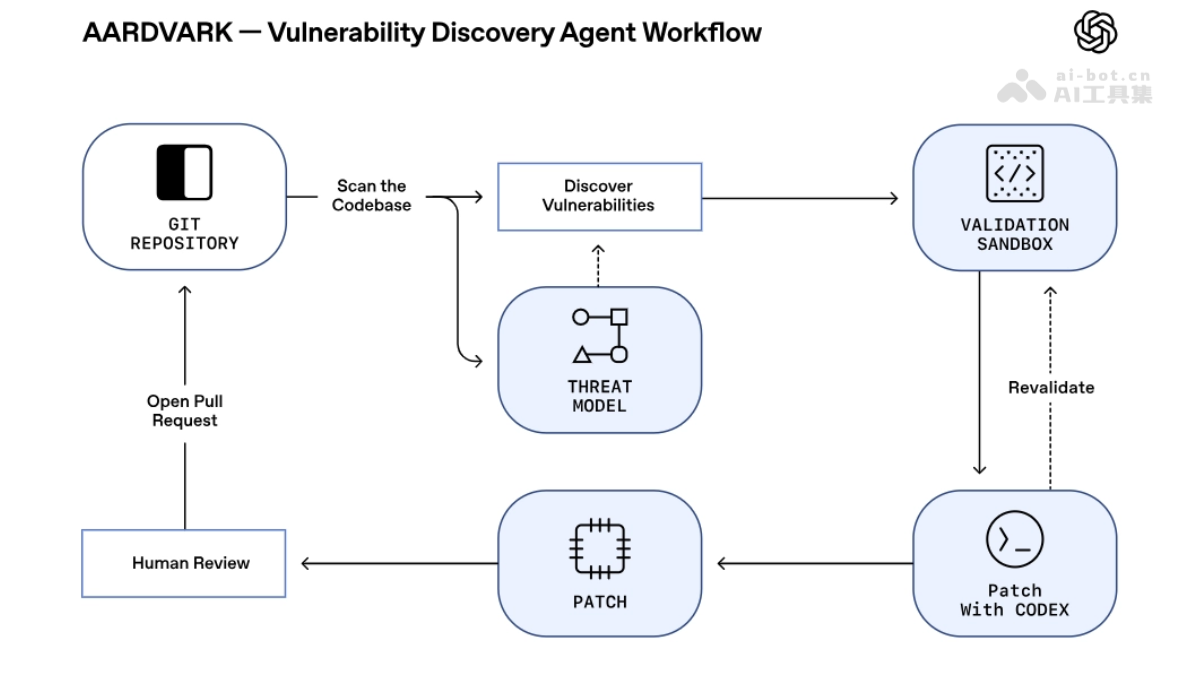
Main Features of Aardvark
-
Vulnerability Identification: Aardvark can automatically analyze source code repositories and accurately identify known vulnerabilities and potential security vulnerabilities, ensuring code security.
-
Risk Assessment: It assesses the exploitability of identified vulnerabilities and classifies severity levels based on risk, helping teams prioritize high-risk vulnerabilities.
-
Remediation Suggestions: It generates targeted remediation plans and patches for each identified vulnerability, helping to resolve issues quickly.
-
Multi-Stage Workflow: Aardvark uses a multi-stage process of analysis, commit scanning, validation, and remediation, comprehensively ensuring the accuracy and efficiency of vulnerability handling.
-
Integration and Collaboration: It can seamlessly integrate with GitHub, Codex, and existing development workflows, supports human review, ensures the accuracy of remediation plans, and does not affect development efficiency.
Technical Principles of Aardvark
-
Driven by Large Language Models: Aardvark is based on GPT-5 large language models, using their powerful reasoning capabilities and tool-calling functions to understand code behavior.
-
Code Behavior Analysis: By reading code, analyzing logic, and writing and running tests, it uncovers vulnerabilities like a human security researcher.
-
Multi-Stage Process:
-
Analysis Stage: Conducts a comprehensive analysis of the entire codebase and generates a threat model reflecting the project's security goals and design architecture.
-
Commit Scanning: Compares code commits with the complete codebase and threat model to detect newly introduced vulnerabilities in real time.
-
Validation Stage: Triggers potential vulnerabilities in an isolated sandbox environment to confirm their exploitability.
-
Remediation Stage: Works collaboratively with OpenAI Codex to generate remediation patches and attach them to detection reports for human review.
-
-
Automation and Human Collaboration: Aardvark provides automated support during vulnerability discovery and remediation, while final remediation requires human review to ensure accuracy and security.
Aardvark Project Address
- Project Website:https://openai.com/index/introducing-aardvark/
- Closed Beta Application:https://openai.com/form/aardvark-beta-signup/
Aardvark Application Scenarios
-
Security Detection for Internal Enterprise Codebases: Aardvark can continuously analyze internal enterprise source code repositories, promptly discover and fix security vulnerabilities, and enhance enterprise security defense capabilities.
-
Vulnerability Discovery and Disclosure for Open Source Projects: Aardvark is applied to open source projects, discovers numerous vulnerabilities through responsible disclosure, and improves the security of the open source software ecosystem.
-
Security collaboration in the development process: Aardvark seamlessly integrates into the development process, collaborates with developers, and provides clear and actionable security insights, ensuring code security while maintaining development efficiency.
-
Detection of hidden issues under complex conditions: Aardvark can accurately identify hidden issues that are triggered only under complex conditions, helping teams discover potential risks in advance.
-
Continuous protection and code evolution: Aardvark continuously evolves with the code, providing teams with continuous protection and ensuring that software remains secure throughout development and maintenance.